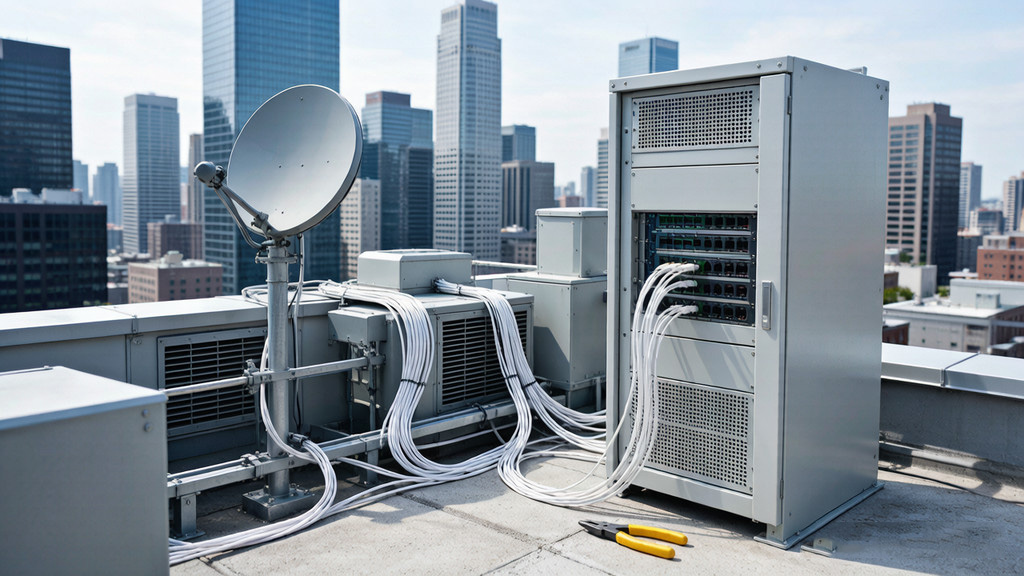
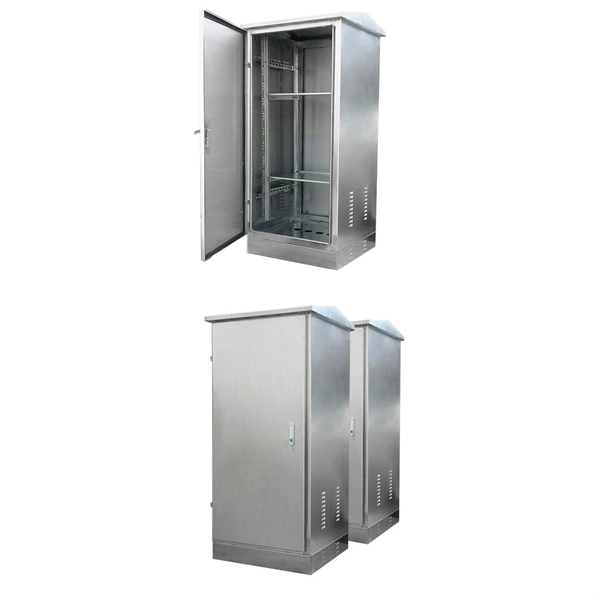
In this guide, you'll learn everything about UL, CE, and ISO certifications, why they matter, and how to choose compliant cabinets for your home or office network. Your home network is more powerful than ever before. A cabinet or rack must belong to one of the following types: Standard 19-in. See Reference Perforated Cabinet. Standard two-post telco rack, with mounting posts. Quick Takeaway: Choosing the right home networking cabinet isn't just about organizing cables—it's about safety, compliance, and protecting your investment. There are two main standards: NEMA (National Electrical Manufacturers Association) in the U. See the charts below for each standard's. Networks are fundamental to the operation, security and resilience of many organisations.
[PDF Version]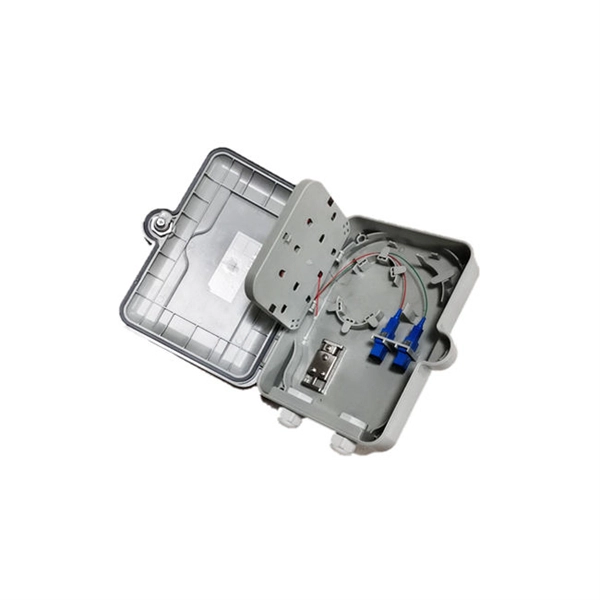
The main types of network security devices include firewalls, intrusion protection systems (IPS), unified threat management (UTM) systems, network access control (NAC), email security gateways, web application firewalls (WAF), and VPN gateways. These devices act as barriers between the internal network and potential threats from the outside world. Whether you're a business owner or an IT professional, understanding the. On top of the many network devices that any enterprise should have today, there are a selection of network security tools and devices that can help you defend your network. While networking security tools have traditionally been implemented as on-prem network security hardware or virtual. Network security solutions are specialized hardware devices designed to protect networks from cyber threats, and modern innovations like Juniper Mist networking for secure, scalable infrastructure further enhance visibility, automation, and overall network performance.
[PDF Version]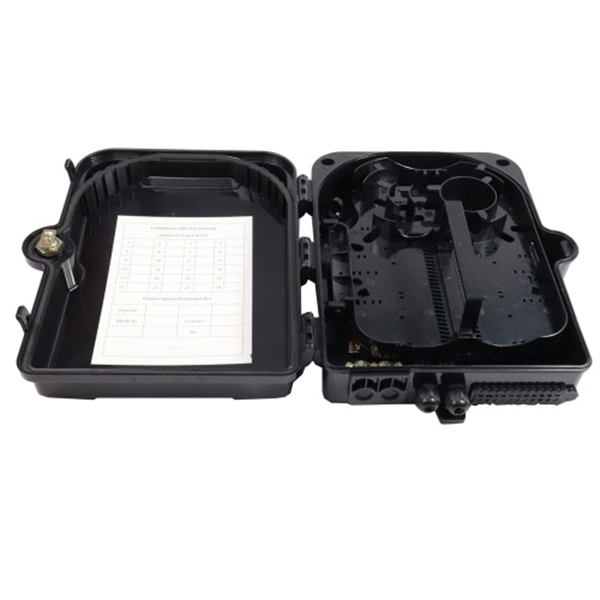
Expired hardware warranties silently increase IT costs, reduce productivity, and expose organizations to security risks. When purchasing multiyear warranties, it is typically cheaper than buying yearly warranties. For example, you can often get a 3-year warranty for the same price as two. Enterprise hardware warranties are designed around manufacturer cycles, not your business goals. The misconception that hardware must be retired when a warranty lapses leads to unnecessary capital. Detailed warranty information and performance metrics allow you to assess the health and longevity of each device, ensuring you make data-driven decisions. Visual network topology maps identify dependencies and bottlenecks, helping you plan upgrades with minimal disruption to operations. The HVMND. To prioritize investments and minimize outages, they must understand factors that affect product life and events that trigger a replacement, then set a strategy for support. This document was last reviewed on 21 June 2016.
[PDF Version]
This section provides an overview of the switch access security features, authentication protocols, and methods. See Using the Management Interface. The authentication, authorization, and accounting (AAA) strategy is used to verify identity of, grant access, and track the actions of remote users in all switches in the Cisco MDS 9000 Family. Network switches operate at the Data Link Layer or Layer 2 of the OSI model. However, that is not enough, because these devices are vulnerable. Switches are a vital security component in networks: After all, they control the traffic for all of your internal data communications.
800G is the latest generation of high-speed optical transmission used to drive high-capacity Ethernet interfaces. The addition of 800 Gigabit per second (Gbps) capability also includes options for 8 lanes ratche.
This report outlines the findings from NSS Labs testing of Fortinet FortiGate-200G Enterprise Firewall which measured the firewall's ability to detect and block exploits, malware, and evasions while maintaining stability and minimizing false positives. In Q2 2025, NSS Labs conducted independent evaluations of leading Enterprise Firewall offerings using the Enterprise Firewall Test Methodology v3. Get deeper visibility into your network and see applications, users, and devices before they become threats. Measure the forward error correction pre-error rate and frame loss rate of each channel in the test environment. Brand Compatibility Test Insert the. The FortiGate 200G Series NGFW combines AI-powered security and machine learning to deliver Threat Protection at any scale.
[PDF Version]
A uni-directional test will be conducted on all pigtail splices with no greater than a. 8 dB after 5 repeated attempts results in the replacement and re-splicing of that pigtail. The primary contributors to measured splice loss are fiber material and design factors that. This provides the tester with the ability to accurately measure the connector loss, connector back reflectance and the adjacent splice loss on a short span (15-30 meters from terminating distribution panel). Pigtail tests taken with long patch cords, or any other “adaptation”, will not be accepted. The instrument injects a pulse of. oss is extremely difficult to construct. Losses at a fiber splice depend on various factors like mode power distributions, attenuation, and mod coupling characteristics of the fibers. These characteristics are difficult to measure experimentally and hence several approximate models have evolved in. The standard for splice loss in optical fiber is typically defined by the International Electrotechnical Commission (IEC) or the Telecommunications Industry Association (TIA).
[PDF Version]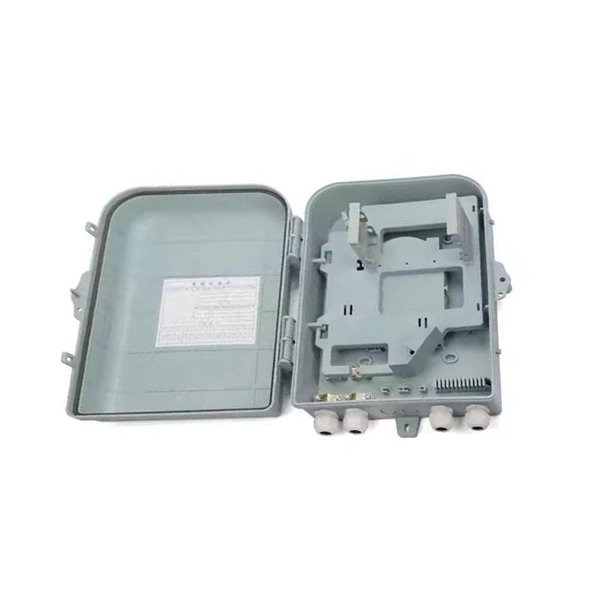
The Plug-on Neutral (PON) system streamlines the installation of electronic breakers by integrating the neutral connection directly into the panel's structural design. Panels designed for PON technology feature a specialized metallic bus bar running parallel to the standard hot. Modern residential systems rely on advanced safety devices like Arc-Fault Circuit Interrupters (AFCI) and Ground-Fault Circuit Interrupters (GFCI) to meet code requirements. With the growing popularity of 4K video streaming, online gaming, VR/AR, IoT, and smart homes, traditional copper broadband is. A passive optical network (PON) is a point-to-multipoint fiber network architecture that uses optical splitters to deliver high-bandwidth services from a single fiber to multiple end users without requiring active electronics in the field.
[PDF Version]Contact us for competitive quotes on any of our fiber optic products
Get a Quote